Enterprise AI Guardrailsfor Innovation-First Enterprises
Governance Meets Performance
Policy-enforced enterprise AI guardrails for regulated organizations
Innovate with the cutting-edge in AI without the drawbacks that come with it. Outsource compliance concerns, auditing, data privacy, and AI security to our enterprise AI guardrails while you focus on AI-powering your business.
Trusted By
Why Regulated Organizations Need Enterprise AI Guardrails
Scale
Hundreds of teams and applications call models every day. Rules set per app drift apart unless one policy layer governs them all.
Regulatory exposure
Regulators ask which policy fired, why it fired, and who was accountable. A content filter alone can't answer those questions.
Data exposure
Prompts carry client records, source code, and trade secrets. Those must be masked before they leave your environment.
Enterprise AI Guardrails for Every Need
Three products run the same enterprise AI guardrail engine, each covering one part of the input and output path.
Walled Protect
Stops prompt injection, jailbreaks, and unauthorized AI use with real-time threat prevention.
Explore Walled ProtectWalled Redact
Masks sensitive data before it reaches external models, including PII, financial data, and trade secrets.
Explore Walled RedactWalled Correct
Validates AI responses against ground truth and flags hallucinations before they reach a user.
Explore Walled CorrectCustomised Policies That Govern Every Team
Our enterprise AI guardrails apply customised policies to both the input and output of every model, with policy packs for each industry and regulated use case.
Risk-policy driven
Configured from your actual risk policies, not a fixed rule set. Every rule is tied to a policy version.
Scoped by department and role
Enterprise RBAC applies different thresholds and escalation rules per department, team, role, or use case, all logged centrally.
Custom Policies
Build policies around your risk appetite, obligations, and approved use cases, per team or application.
Breeze Through Every Regulator Audit
Basic guardrails that only filter content aren't enough when your regulator asks which policy fired, why, and who was accountable for it. Our enterprise AI guardrails log every interaction and every decision with the policy applied and the outcome, so your audit team can answer those questions from the record.
- Every decision is recorded with user identity, role, the policy version applied, and the outcome.
- Masked, blocked, escalated, and passed interactions are all logged, not just the failures.
- Evidence packages are exportable for internal audit, external auditors, and regulators.
- The Governance Dashboard rolls enforcement data up into board-ready posture reports.
Mapped to
Stay in Control with Human in the Loop
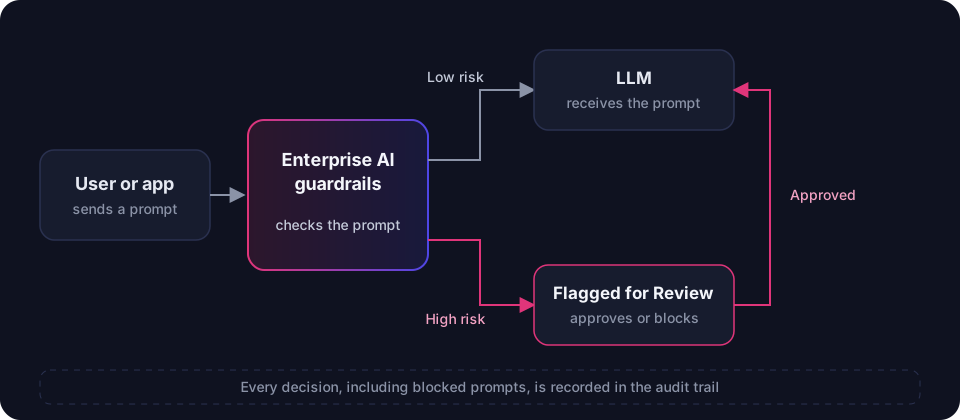
- Our enterprise AI guardrails flag high-risk prompts and hold them for human review.
- The review decision is captured in the audit log, satisfying human-oversight obligations for high-risk AI.
Enterprise AI Guardrails for Autonomous Agents
Agentic workflows in regulated industries can trigger dozens of LLM calls per task, and each one unguarded is a compliance risk. Claims triage, KYC review, and clinical summarization all need every agent-to-LLM call governed and audited.
Our enterprise AI guardrails sit at the infrastructure layer, intercepting every agent-to-LLM call with the same policy enforcement and audit trail you apply to human interactions. No exceptions, no blind spots.
Intercept every agent call
Capture each agent-to-LLM API call, not just the user-facing turn or final output.
Escalate high-risk chains
Multi-hop reasoning that crosses risk thresholds goes to human review before the agent commits to an action.
One unified audit trail
Human-initiated and agent-initiated interactions sit in the same audit trail, under the same policies.
Zero Data Privacy Compromise
Your guardrails policy, masking rules, and audit logs should never leave your perimeter. Our enterprise AI guardrails run inside your boundary, and nothing is streamed to a third-party cloud unless you explicitly choose it.
On-premise
Runs in your data center. Policies, decisions, and logs stay entirely within your infrastructure.
Private cloud
Deployed in your own VPC or sovereign cloud region, under your keys and your data residency rules.
Air-gapped
Fully disconnected operation for classified, defence, and government workloads with maximum isolation.
Adopt Enterprise AI Guardrails Adapted to Your Industry
One proven enterprise AI guardrail engine, with industry-specific policy configurations that map to your sector's regulatory requirements and risk profile.
Banking
Customer-facing chatbots are blocked from providing unlicensed financial advice or fabricating account statements, with every block logged against MAS TRM and FCA control references.
Healthcare
Clinical AI is guardrailed to summarise and document, never diagnose or prescribe, with HIPAA-aligned audit logging.
Public Sector
Agency AI assistants are scoped to approved use cases with escalation for anything outside policy, producing the record-keeping evidence oversight bodies request.
Financial Services
Investment advisories and lending decisions are guardrailed to prevent discriminatory bias, model hallucination, and compliance violations under SEC and regional AI governance frameworks.
Legal
Legal research assistants are bounded to approved case law databases and prevented from generating novel legal theories without human review.
Insurance
Underwriting and claims processing AI is guardrailed against discriminatory bias, model hallucination, and fraud detection errors, with full audit trails.
Ready to Deploy Enterprise AI Guardrails?
Talk to us about your existing risk policies and map them into enterprise AI guardrails your teams can deploy.
Learn More About Enterprise AI Guardrails
AI Audit Logs for Compliance: What Regulators Expect Enterprises to Capture
The fields regulators look for in AI audit logs, and how to capture them from the start.
AI Governance in Financial Services: Controls for Banks Using ChatGPT and Copilot
The controls banks need when staff use ChatGPT and Copilot, from access to monitoring.
Responsible AI Framework: The Governance Pillar Every Enterprise Needs
How to build the governance pillar of a responsible AI program across an enterprise.
You May Also Like
Enterprise RBAC
→Department-level AI access controls to manage who can use which models and for what purposes.
Data Classification
→Automatically classify data sensitivity across all AI interactions for better governance.
Governance Dashboard
→Real-time monitoring and compliance reporting across every LLM interaction in your organization.
Frequently Asked Questions
What makes enterprise AI guardrails 'enterprise-grade' for a regulated company?
Three things a generic guardrail library doesn't give you: guardrails configured from your actual risk policies rather than a fixed rule set, an audit trail a regulator or internal audit team can rely on for every decision the guardrail made, and human-in-the-loop escalation for anything below your confidence threshold. WalledAI's guardrail engine is built around those three requirements first, with the technical filtering underneath.
How do WalledAI's guardrails map to compliance frameworks?
Every guardrail decision - a masked entity, a blocked prompt, an escalation - is tagged with the policy version and control it satisfies, pre-mapped to MAS TRM, the EU AI Act, NIST AI RMF, ISO/IEC 42001, PDPA, and SOC 2. Compliance teams get defensible evidence instead of screenshots assembled after the fact.
Are these guardrails a separate product from Walled Protect and Walled Redact?
No. Enterprise AI Guardrails is how regulated buyers deploy the same WalledAI runtime engine - Walled Protect's content and prompt-injection guardrails plus Walled Redact's masking - with compliance-specific policy packs, escalation workflows, and audit reporting layered on top. There is one engine, one integration, one audit trail.
Can guardrail policies differ by department or use case?
Yes. Enterprise RBAC scopes guardrail policy to department, team, role, and use case, so a customer-facing chatbot, an internal coding assistant, and a claims-processing agent can each run under different thresholds and escalation rules, all logged centrally.
Show all FAQsShow fewer questions
Does WalledAI support human oversight requirements for high-risk AI?
Yes. Configurable confidence thresholds route uncertain or high-risk outputs to human reviewers before they reach an end user, satisfying human-oversight obligations under the EU AI Act, MAS TRM, and NIST AI RMF, with the review decision captured in the audit log.