AI Governance Dashboardfor Real-Time Risk Monitoring and Audit-Ready Compliance
Gain complete visibility and control over every prompt, across every model.
Live demo in under 24 hours · No commitment required
- SOC 2 Type II
- ISO 27001
- GDPR
- PDPA
Trusted By
Govern Every Model, Gauge Every Interaction
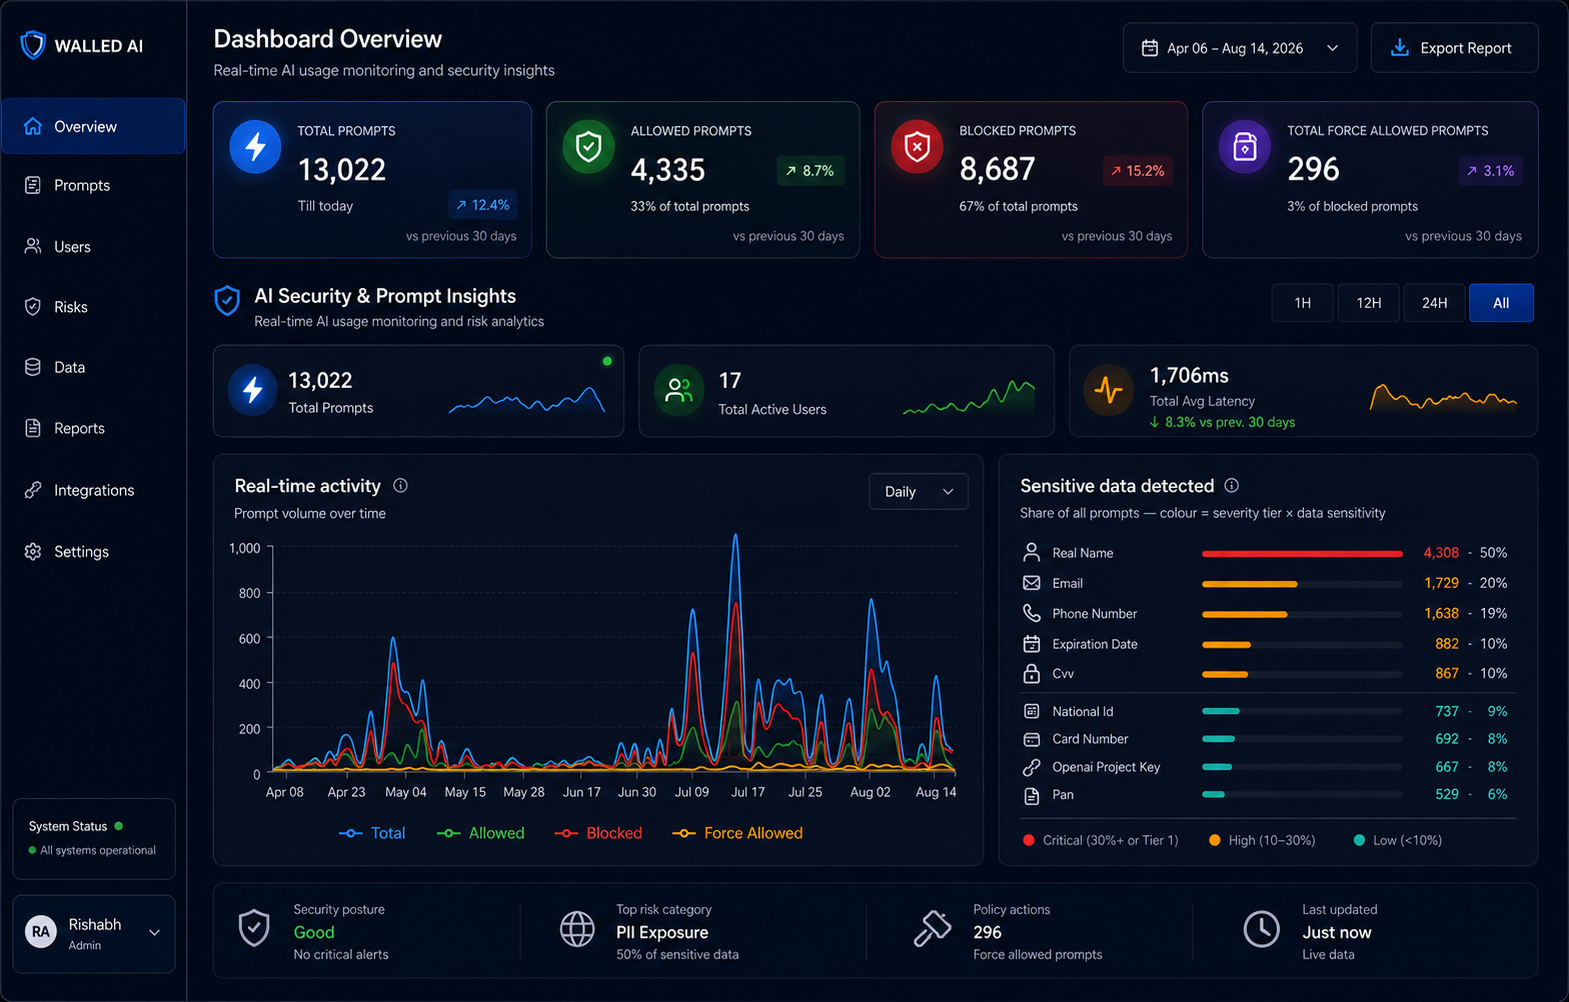
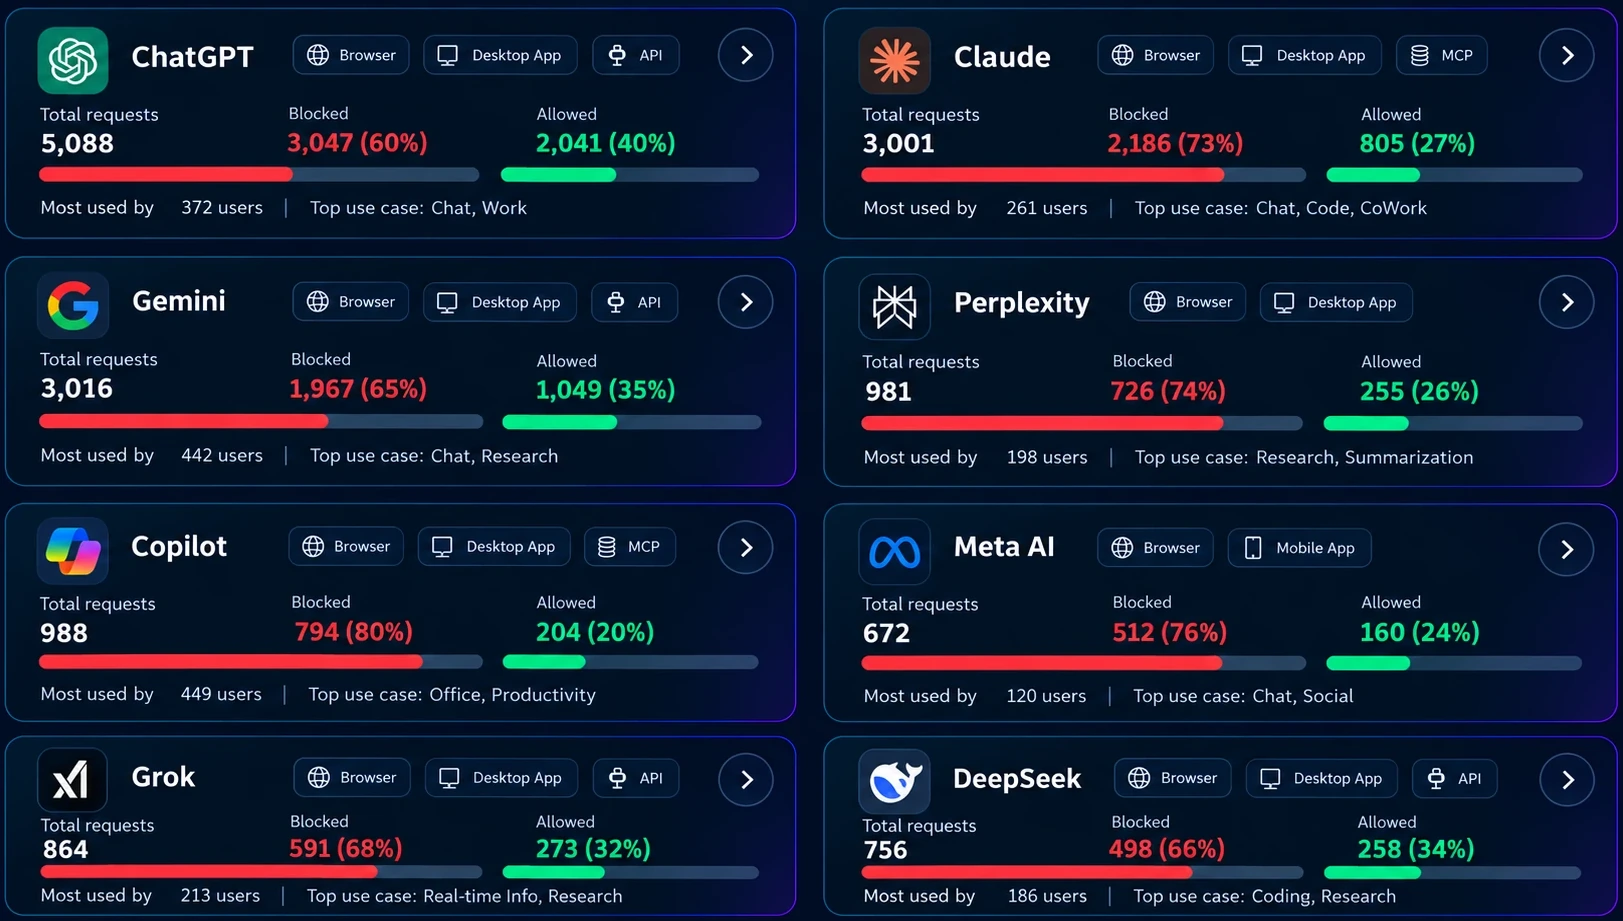
Monitor LLM activity across every interaction and measure how your defence is holding up. Track prompts across ChatGPT, Claude, Gemini, Perplexity, Copilot, Meta AI, Grok, DeepSeek, or your own internal AI. Measure prompt volume, record policy decisions, and gain a much needed bird's eye view of organisational LLM activity.
From AI Policy to Actual Controls in an Afternoon
Turn policy documents into machine-enforceable live controls that keep your AI systems in check. Move from policy to carefree compliance in an afternoon with automated onboarding that turns documents into department-specific risk profiles, role-based access controls, and real time AI controls in an instant.
Upload policies
Extract controls
Create department risk profiles
Enforce policies in real time
Report governance outcomes
Upload policies
Acceptable use, data classification, and regulatory requirements go in as documents.
Upload policies
Acceptable use, data classification, and regulatory requirements go in as documents.
Extract controls
Create department risk profiles
Enforce policies in real time
Report governance outcomes
Centralized Dashboard for Complete Collaboration
Organizational AI activity is scattered across assistants, copilots, agents, and internal applications. WalledAI turns that fragmented activity into a central governance view enabling every team to work from a single source of truth.
See Every AI Interaction
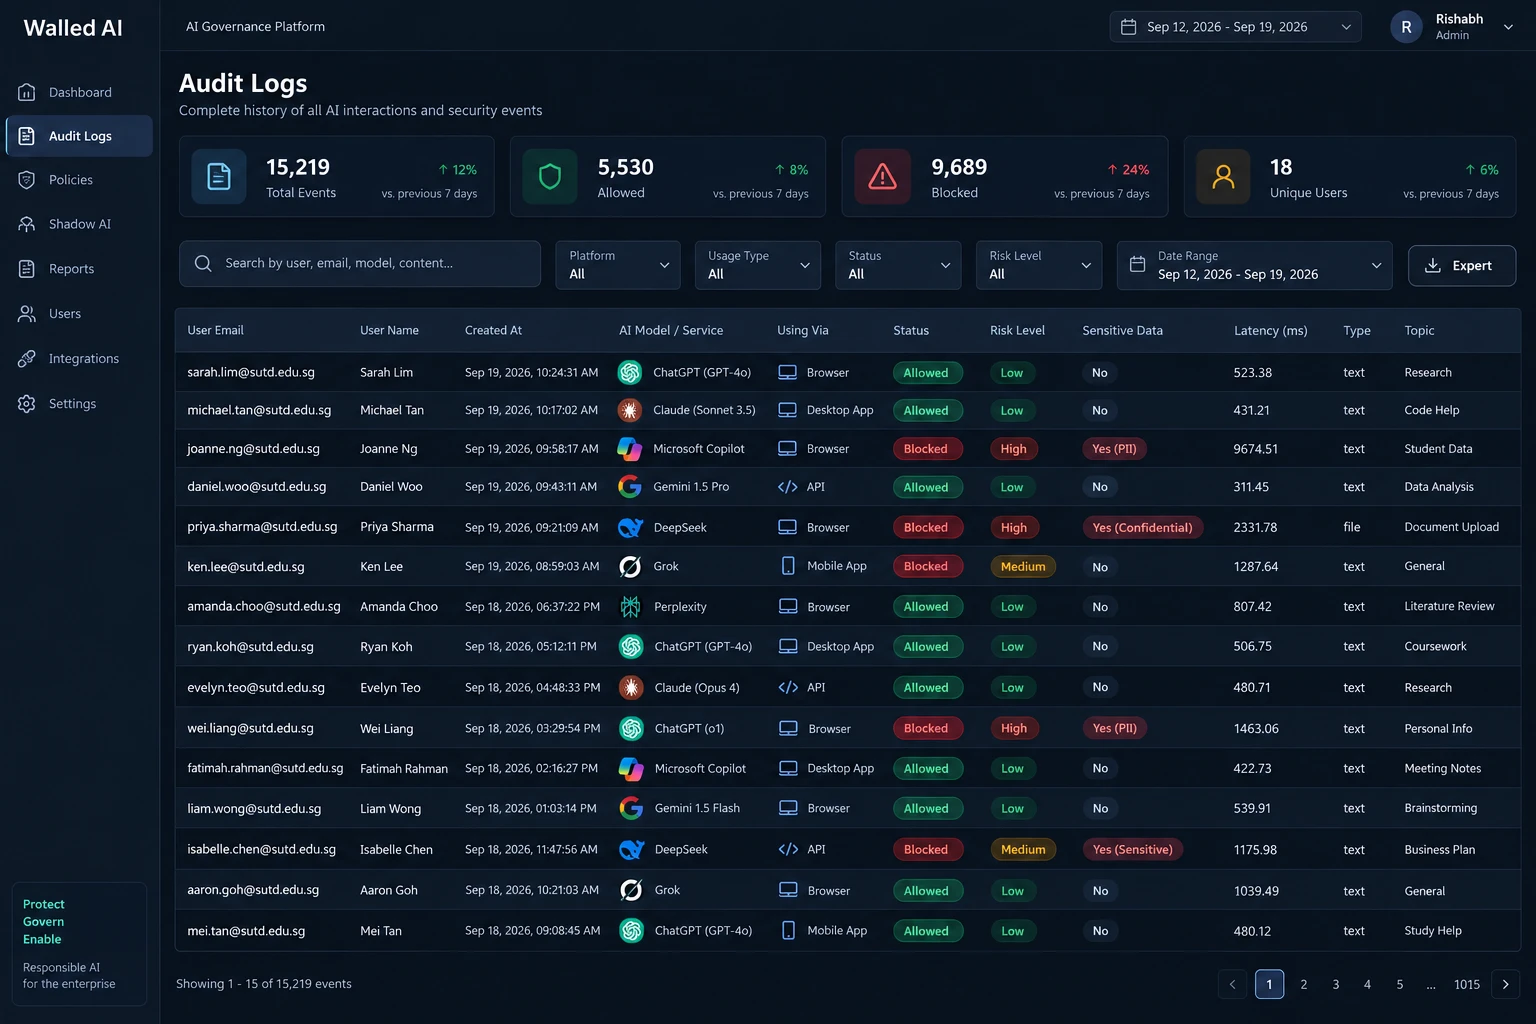
Track AI usage across ChatGPT, Claude, Copilot, internal copilots, AI agents, and approved enterprise tools. Identify who is using AI, where it is used, and what data risk is involved.
AI Governance Visibility for Everyone Accountable
Your security team needs to know where risk lives. Your compliance team needs to prove everything was governed. Your board needs confidence in your AI adoption. With Walled AI, you can meet everyone's needs from a single dashboard.
CISO and Security Leaders
Compliance and Risk Teams
Board and Executive Stakeholders
IT and Platform Teams
Preparing for an AI Governance Board Review
A regulated enterprise needs to show its board how employee and application AI usage is governed. Instead of collecting reports manually, security and compliance teams can show the board a live, defensible view of AI governance. The same reporting layer backs multiple business units like legal and manufacturing. Each unit can prove how its AI use was governed simply by collating relevant metrics like:
AI adoption by business unit
Interaction volume and active users per function, trended over the reporting period.
Sensitive-data events prevented
Detections and redactions applied before prompts reached an external model.
Open policy exceptions
Approved deviations, their owners, and their review dates.
Top risk trends
The violation categories moving fastest, with the teams driving them.
Compliance control coverage
Which controls in your chosen frameworks currently have supporting evidence.
Downloadable evidence package
Audit trail extracts and enforcement records packaged for reviewers.
Audit-Ready AI Compliance Reporting
Enable audit-ready AI compliance by mapping real-time dashboard evidence to the governance needs of your organisation. Evidence is generated from the controls already enforcing your policies, including role-based AI access controls and sensitive-data redaction at runtime.
EU AI Act
European UnionRisk classification, transparency, and high-risk system oversight evidence.
NIST AI RMF
United StatesGovern, Map, Measure, and Manage functions supported by live enforcement records.
ISO 42001
GlobalAI management system controls with documented policy and review history.
SOC 2 Type II
GlobalSecurity, confidentiality, and processing integrity evidence for AI workflows.
HIPAA
United StatesProtected health information handling and redaction records for AI use.
MAS TRM
SingaporeTechnology risk management controls for AI in regulated financial institutions.
PDPA
Singapore / ASEANPersonal data handling, consent boundaries, and retention evidence.
* Walled AI supports your own audit and attestation work; it does not provide automatic certification or guarantee compliance.
Move Beyond Mediocre AI Analytics
Stuck with simple AI usage analytics? Move to WalledAI and experience enterprise-grade AI governance with real-time enforcement, comprehensive audit trails, and a host of other features that ordinary analytics tools cannot match.
| Capability | Basic AI usage analytics | Cloud-only AI governance tools | WalledAI Governance Dashboard |
|---|---|---|---|
| Multi-model AI visibility | Partial | Partial | Yes |
| Real-time policy enforcement | No | Partial | Yes |
| Pre-LLM sensitive-data protection | No | Partial | Yes |
| Immutable audit trail | No | Partial | Yes |
| On-premises and air-gapped deployment | No | No | Yes |
| Board and regulator reporting | No | Partial | Yes |
| Custom policy and risk profiles | No | Partial | Yes |
And Tap into More Meaningful Metrics
AI interactions by department and team
Spot which business units are scaling AI fastest and prioritise governance reviews there first.
Approved and unapproved AI tool usage
Bring shadow AI into policy scope or block it before it becomes an unmanaged data channel.
Sensitive data detections and redactions
Quantify what never left your environment, and tighten classification rules where detections cluster.
Policy violations and risk trends
Target training, access changes, or stricter guardrails at the teams generating repeat violations.
Regulatory control coverage and compliance gaps
See which controls have evidence and which still need owners before an audit window opens.
Audit trail completeness and evidence readiness
Confirm you can produce a defensible record on request instead of assembling it after the fact.
Enable Effortless AI Risk and Compliance Visibility Today
Get a live view of AI usage, policy enforcement, compliance evidence, and emerging risk across every AI interaction.
AI Governance Success Stories
Global Investment Bank Secures Client Data
Healthcare Provider Enables AI Without PHI Exposure
Law Firm Accelerates Deal Review with Protected Data
Learn More about AI Governance
AI Governance Frameworks and Standards
Navigate NIST AI RMF, EU AI Act, ISO 42001, SOC 2, HIPAA, and MAS TRM governance requirements - and how to map your controls to each.
Measuring AI Governance ROI
Why implementing live AI governance delivers 10x returns through reduced risk, faster compliance, and smarter resource allocation.
Building a Defensible AI Audit Trail
What boards and regulators expect to see from your AI governance evidence - and how to make it immutable, searchable, and exportable.
You May Also Like
Walled Redact
→Multi-modal PII masking for AI prompts. Protect all sensitive data across 50+ entity types.
Walled Protect
→Stop prompt injection, jailbreaks, and unauthorized AI use with 99.7% blocking accuracy.
Walled Correct
→Validate AI responses against ground truth, reduce hallucination rates from 12% to 0.3%.
Data Classification
→Automatically classify data sensitivity across all AI interactions.
Enterprise RBAC
→Department-level AI access controls, control who can use which LLMs.
Shadow AI Detection
→Discover and block unauthorized AI usage across browsers, networks, and SaaS.
AI Governance Dashboard FAQs
Can an AI governance dashboard help prove governance progress to the board?
Yes. WalledAI gives board and executive stakeholders visibility into AI adoption, sensitive-data events prevented, open policy exceptions, compliance control coverage, and governance progress over time.
What does an AI governance dashboard show?
An AI governance dashboard shows how AI is actually used across the organisation: interactions by department and team, approved versus unapproved AI tools, sensitive data detections and redactions, policy violations and risk trends, regulatory control coverage, and the completeness of the audit trail behind every interaction.
How does an AI compliance dashboard help security and compliance teams?
It replaces manual evidence collection with a live record. Security teams see where risk is concentrated and which controls are firing; compliance teams pull enforcement records, exception lists, and control coverage mapped to the frameworks they report against, without chasing screenshots from individual tool owners.
Can WalledAI monitor ChatGPT, Claude, Copilot, and internal AI applications?
Yes. WalledAI sits in front of the model rather than inside it, so the same governance dashboard covers commercial assistants such as ChatGPT, Claude, and Copilot, internal copilots, AI agents, and applications calling models through the WalledAI gateway or browser plugin.
Does the dashboard provide audit trails for AI interactions?
Every governed interaction is logged with timestamps, the policy evaluated, the enforcement decision taken, data classification results, and the acting role. Records are append-only, searchable, and exportable as an evidence package for internal audit or a regulator.
Can WalledAI create board-ready AI governance reports?
Yes. The dashboard generates executive summaries covering AI adoption by business unit, sensitive-data events prevented, open policy exceptions, top risk trends, and control coverage, so a board review is a live, defensible view rather than a manually assembled deck.
Can the AI governance dashboard support EU AI Act, HIPAA, SOC 2, MAS TRM, and ISO 42001 programmes?
WalledAI maps dashboard evidence and enforcement records to the control requirements your programme is built on, including the EU AI Act, NIST AI RMF, ISO 42001, SOC 2 Type II, HIPAA, MAS TRM, and PDPA. This supports your own audit and attestation work; it is not automatic certification and does not guarantee compliance.
Can WalledAI be deployed on-premises or in an air-gapped environment?
Yes. WalledAI is designed for on-premises, private cloud, and fully air-gapped deployment, so governance telemetry, audit logs, and policy data stay inside your environment. No customer data is used to train models.